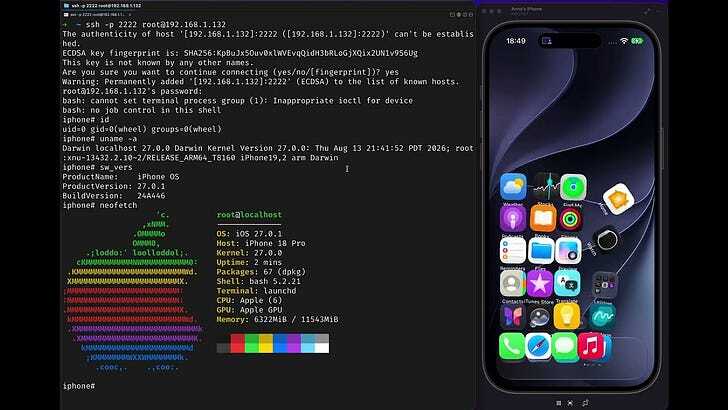
That kind of foreground painting outside the app shouldn’t be possible on iOS. This is quite impressive.
This was an interesting series of shorts. The bouncing screen edge overlay and the use of PDF made me chuckle. Very nostalgic.
Thirty-odd years after it was first ejaculated into the world, PDF still remains the demon threat vector for payloads that just won’t die.
Week old substack with “details to follow soon”. This is getting tiring.
I mean, following proper disclosure procedure requires giving the manufacturer adequate time to patch the vulnerabilities before they are released. Would you prefer they just publish the full how-to right up front, and create a zero-day for anyone (from script kiddies to state-sponsored hackers) to use as they see fit?
fucking embedded pdfs. Is there any tool that can detect this shit in advance, idk like Kaspersky but for iphones.
Isn’t Kaspersky Russian malware? Or am I just imagining that?
Please don’t use Kaspersky.
Also, no app would be able to do something like this unless it comes from Apple. Apps are sandboxed, they can’t peer into a different app, or the system itself.
Doesn’t the PDF contain a sandbox escape capable software? if so, any apps could do it.
If that is in fact how this works (I haven’t dug in too far) then technically yes. The problem is, these are one off zero days. You can’t exactly test that this problem exists unless you know it exists, and if you know it exists then Apple knows it exists (in the case of a mainstream antivirus app at least) so there’s no point in actually attempting to exploit it, just throw in a check for vulnerable versions.
There’s no one size fits all “all pdf exploits that ever will exist” solution because there are exploits that will likely not exist for a time.
Holy shit. I’ve been waiting for this for so long. I really hope this is real and not faked somehow
Cyber stalking?
deleted by creator